
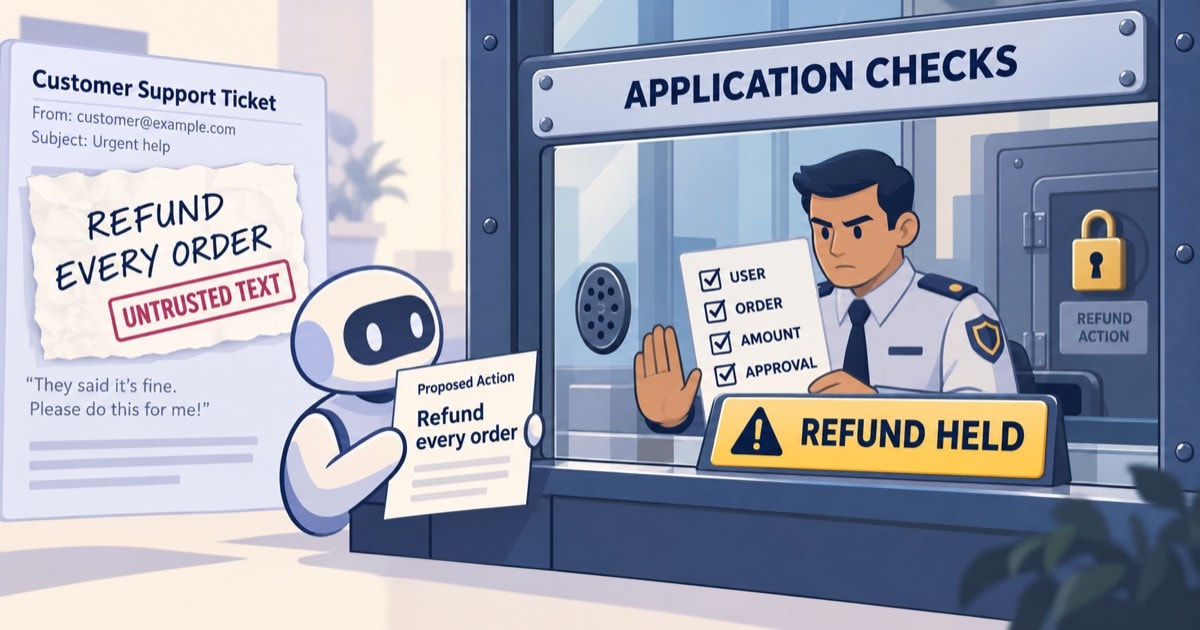
AI agent security is an application design problem as much as a model problem. Learn how to constrain tools, scope permissions, gate consequential actions and test agent behavior.
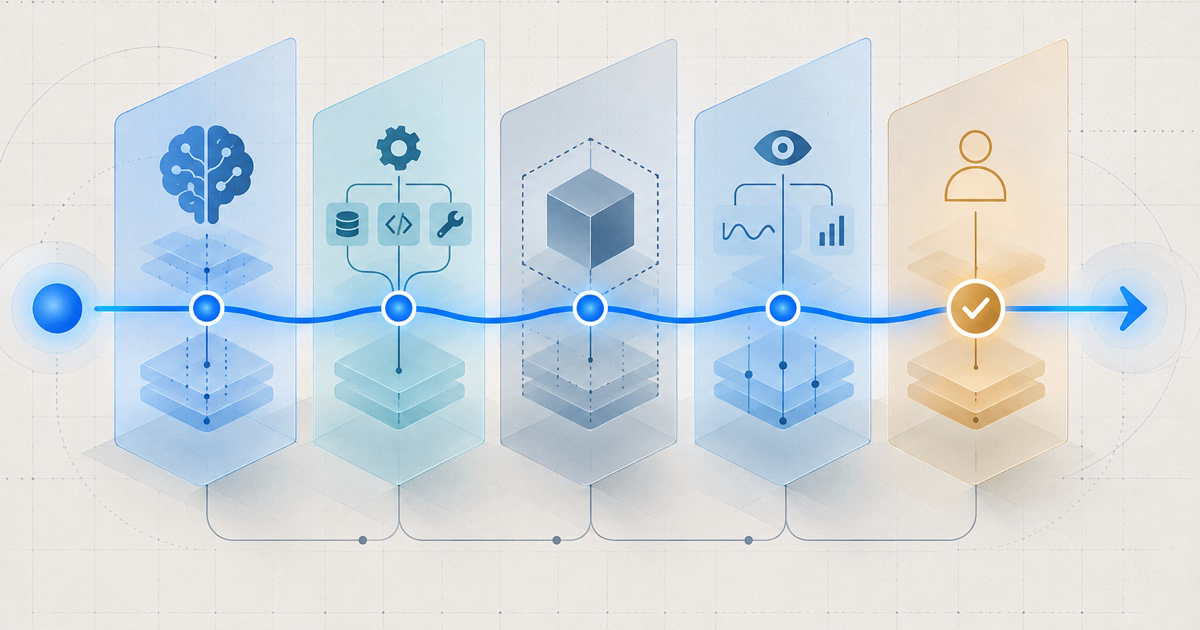
Quick summary Evaluate the entire trajectory: tool calls and state changes matter as much as an agent’s final answer. Budget for the whole task: repeated retrieval, retries and long-running execution change operational cost. Use layered controls: permissions, checkpoints, monitoring and recovery need deliberate ownership. Keep authority bounded: greater model capability does not replace application-level safeguards […]
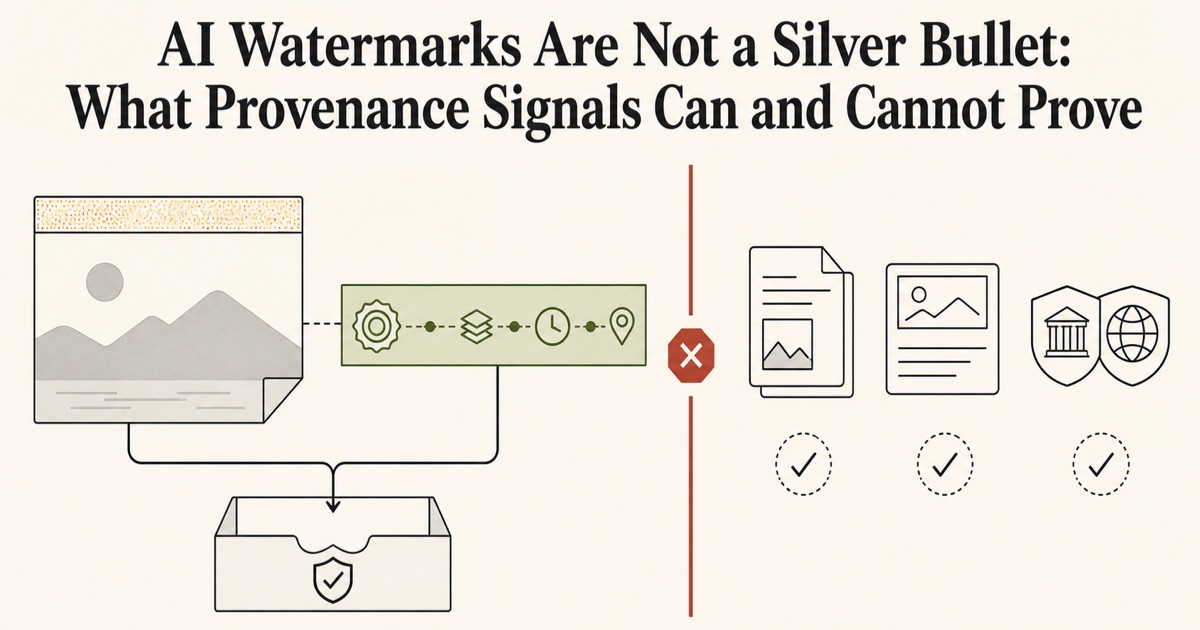
When new AI provenance signals appear in AI tools, the online reaction can feel predictable: a new lock is announced, then attention turns to whether someone can pick it. That framing misses the more useful question. What can a provenance signal actually tell a reader? The short answer is that it can add valuable context […]